-
- Products
- Indoor Household Cords
- Appliance Cords
- General Purpose Short-Length Cords
- General Purpose Extension Cords
- Landscape & Decorating Cords
- Bright Color Extension Cords
- Oil-Resistant Extension Cords
- Cold-Flex Extension Cords
- VividFlex Power Cords
- EXTREME All-Weather Cords
- Cord Management
- Task Lights
- Adapters & GFCI Devices
- Where to Buy
- About
- Careers
- Glossary
- Catalog

10 Tips for Choosing the Right Embedded Computer
Choosing the right Embedded Computer is rarely a simple matter of comparing processor speeds. A reliable decision begins with the machine’s real working environment. Will it operate inside a dusty factory cabinet, a refrigerated vehicle, or a sealed medical device? Each setting changes the requirements for cooling, enclosure strength, power input, and long-term stability.
A practical evaluation should examine processing needs, available I/O, storage options, operating-system support, network performance, and expansion capacity. Datasheets provide essential specifications, but hands-on testing often reveals more. Engineers should check boot times, thermal behavior, vibration resistance, and performance under continuous workloads. A compact unit may look efficient on a workbench, yet become difficult to service after installation. That detail matters.
Lifecycle support deserves equal attention. Industrial systems may remain active for seven years or longer, so component availability and firmware maintenance can influence total cost. Certifications, security features, and supplier responsiveness also help establish trust. Ask direct questions. Get written answers.
No checklist is flawless. A team may select a powerful processor and overlook connector placement, fan noise, or unstable power at the site. That mistake can delay deployment and increase maintenance costs. These ten tips connect technical specifications with practical evidence, helping readers compare Embedded Computer options with greater confidence. The goal is not to choose the most impressive model. It is to choose a dependable platform that fits the application, the environment, and the people responsible for keeping it running.
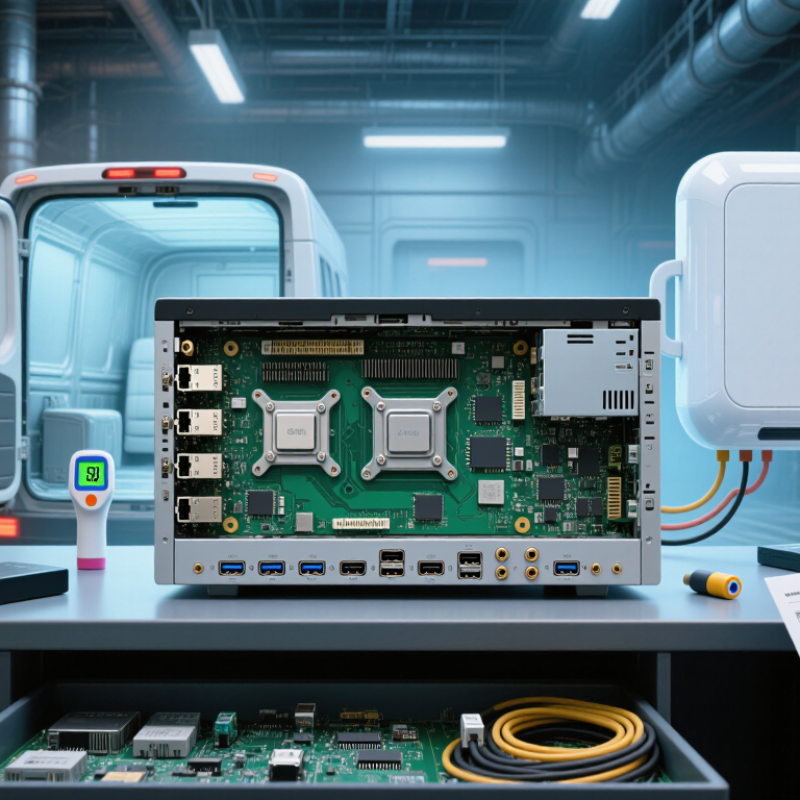
Table of Contents [Hide]
Define Workloads with CPU Benchmarks, TDP, and 24/7 Duty-Cycle Targets
10 Tips for Choosing the Right Embedded Computer
Define the workload before comparing processor numbers. A vision system may need sustained image processing, while a controller may spend most of its time idle. Use CPU benchmarks that resemble the real application, not only synthetic scores. Test the actual software, data size, and input rate. A higher score can still disappoint when memory access becomes the bottleneck.
Tip 1: Measure sustained performance, not short bursts. Run the computer for several hours and record response time, temperature, and throttling.
Tip 2: Treat TDP as a thermal planning value, not a complete power guarantee. Enclosures, airflow, ambient heat, and storage devices can raise the final load. In a sealed cabinet, even a modest processor may need a heat spreader or lower operating limit.
Tip 3: Set a clear 24/7 duty-cycle target. Continuous operation demands stable performance, predictable cooling, and components rated for long service. Include startup cycles, peak workloads, and recovery after power interruptions.
My early estimates were too optimistic because I tested average loads instead of worst-case bursts. That mistake changed the design. Leave practical headroom, but do not oversize blindly; unused processing capacity can increase heat, cost, and power consumption.
Document benchmark settings, thermal conditions, and failure observations so another engineer can reproduce the decision.